A firewall is a network security device designed to monitor, filter, and control incoming and outgoing network traffic based on predetermined security rules. The primary purpose of a firewall is to establish a barrier between a trusted internal network and untrusted external. Network firewalls inspect and control traffic based on security policies — blocking unauthorized access, filtering threats, and segmenting networks to limit lateral movement after a breach. While most computers have software firewalls installed, other devices lack their own security.
Network monitoring tools track network performance, device health, and security in real-time. Open source options like Zabbix, Nagios, and OpenNMS provide free alternatives to commercial tools like SolarWinds and PRTG. We've shortlisted 21 of the very best in this comprehensive guide. It will help in managing and controlling the network. These tools monitor bandwidth, latency, and device status using SNMP, agents, or. Network security monitoring tools are tools designed to prevent misuse of the organization's network through continuous monitoring. Network visibility platforms, vulnerability management scanners, SIEM and threat detection platforms, next-generation firewalls.
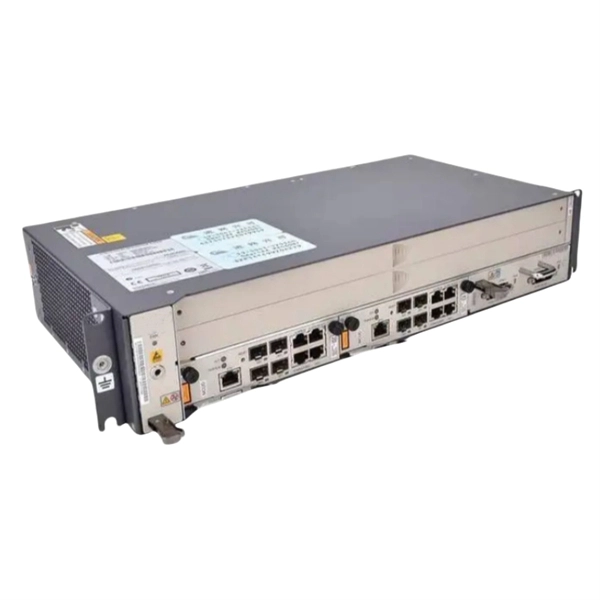
A firewall is a Layer 4 security device that protects the network perimeter by filtering traffic based on IP addresses, ports, and protocols. Network security involves tools, techniques, and policies to protect digital assets from unauthorized access and cyber threats. It combines hardware, software, and expert resources to ensure network integrity and prevent breaches. By employing multiple graded protection stages, potential unauthorized access and data breaches can be diffused. In this lesson, we examine the network firewall - a security device that operates at Layer 4 of the OSI model and guards the perimeter of the network. The following diagram shows the most common icons used to visualize a Cisco firewall in the network topology.
A firewall is a network security solution that protects your network from unwanted traffic. Firewalls block incoming malware based on a set of pre-...
Web Application FirewallUnified Threat Management FirewallNetwork Address Translation FirewallsInternal Segmentation FirewallsNext-Generation Firew...
Without a network firewall, network security is compromised, and your organization is wide open to bad actors who could steal or compromise your da...
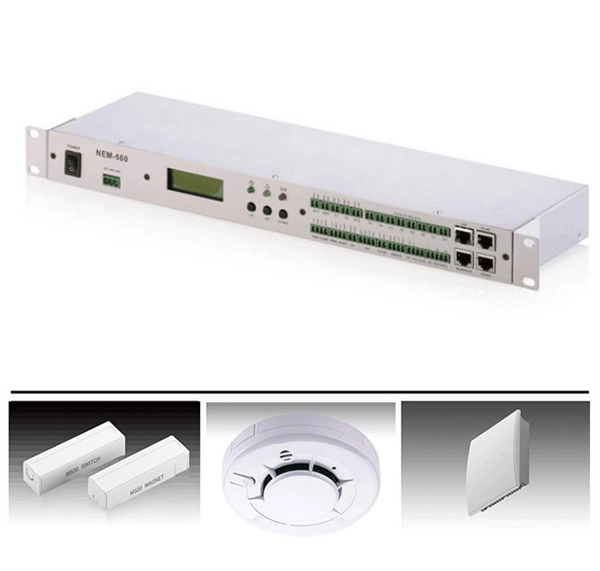
By automating transformers, MVD systems, LV panels, and PFC systems, utilities can minimize energy wastage, improve safety measures, and make their infrastructure more resilient. ● Other distribution automation applications such as Direct Transfer Trip. The guide also provides details on the system's overall structure, different ways it can be deployed, specific deployment instructions, recommended best practices, and potential challenges you might face during. Abstract: This article examines the role of automation in modern power distribution systems as a critical solution for improving energy security, operational efficiency, and grid reliability. Our engineers are experts at multifunction microprocessor-based relay technology, and we design protection schemes for generation, transmission, distribution, and low-volt ge systems worldwide. It also reveals some trends and future.
[PDF Version]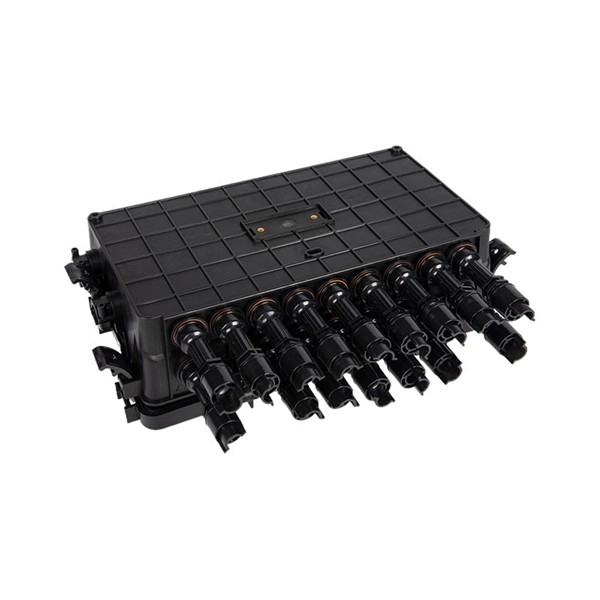
Assess specific security requirements based on factors such as data sensitivity, regulatory compliance, and potential threats. Consider the size and scope of the network to determine the appropriate network security hardware. 50002 of the Commission's rules directs the Public Safety and Homeland Security Bureau to publish a list of communications equipment and services (Covered List) that are deemed to pose an unacceptable risk to the national security of the United States or the security and safety of United. Before diving into enterprise network security best practices, let's review the common types of network devices and security solutions that organizations can take advantage of: Bridges were once used to connect two or more hosts or network segments. They are outdated and no longer used. Hubs were. In today's rapidly evolving digital landscape, network security consultants are challenged to consistently evaluate and select optimal security solutions to protect computer networking products.
[PDF Version]
Tools like Rapid7 InsightVM provide automated asset discovery, risk prioritization, and continuous monitoring. Real-time attack surface visualization involves mapping all potential entry points for cyber attackers. By visualizing these factors, we can quickly detect and respond to potential threats. Network security devices are specialized tools used to safeguard computer networks from unauthorized access, cyber threats, and potential attacks. This technique helps in understanding complex data, identifying patterns, and improving network management by providing a clear visual. Controlling the communication of devices within a network by compartmentalization or segmentation is one of many techniques to protect and improve the overall security of networked systems. Occasionally, businesses purchase commodity server hardware and install custom software to create their own network security device.
[PDF Version]Contact us for competitive quotes on any of our fiber optic and telecom products
Get a Quote